Worcester, Massachusetts
Cybersecurity Solutions for Worcester Organizations
Security Built In From Day One
Triton Technologies is a cybersecurity-first managed IT company headquartered at 35 Harvard Street in Worcester since 2001. Every client gets the same security standard: Sophos Firewall at the perimeter, Sophos Endpoint with XDR on every device, multi-factor authentication on every account, and backups with documented restore tests based on your compliance requirements.
Triton is a Sophos Silver Partner, and every technician on our team is Sophos trained and certified. Worcester is a city of hospitals, colleges, research labs and manufacturers. Those organizations hold patient records, student data, intellectual property and controlled defense information, which is exactly what attackers go after.
The Security Layers We Deploy and Manage
Each layer is deployed, monitored and tuned by our team, not installed and forgotten:
- Sophos Firewall at the perimeter, with intrusion prevention and web filtering, including virtual editions in AWS or Azure so cloud networks meet the same standard
- Sophos Endpoint XDR on every device, monitored around the clock and able to isolate a compromised machine automatically
- Proofpoint email filtering that blocks phishing and business email compromise
- Multi-factor authentication and conditional access for Microsoft 365
- Least-privilege access: staff get only the permissions their work requires
- Network segmentation that separates clinical, research, guest and payment systems
- Backups with Datto and Triton Online Backup, stored in AWS, Wasabi or other S3-compatible storage
- Security awareness training with Proofpoint, or yearly Sophos training for lighter compliance needs
In business since, Worcester, MA
Average time to first response
Of MSPs for service performance (MSPbots benchmark)
Client satisfaction
Of clients with us five years or more
Offices across the US, Ireland and the BVI
Our Free Security Assessment
Every new client relationship starts with a free, read-only security assessment. We review your Microsoft 365 configuration, which usually takes about a day, and sweep your internal network over a secure VPN or with a device we leave on site, which takes about a week. The sweep covers device configuration, firmware levels and network security.
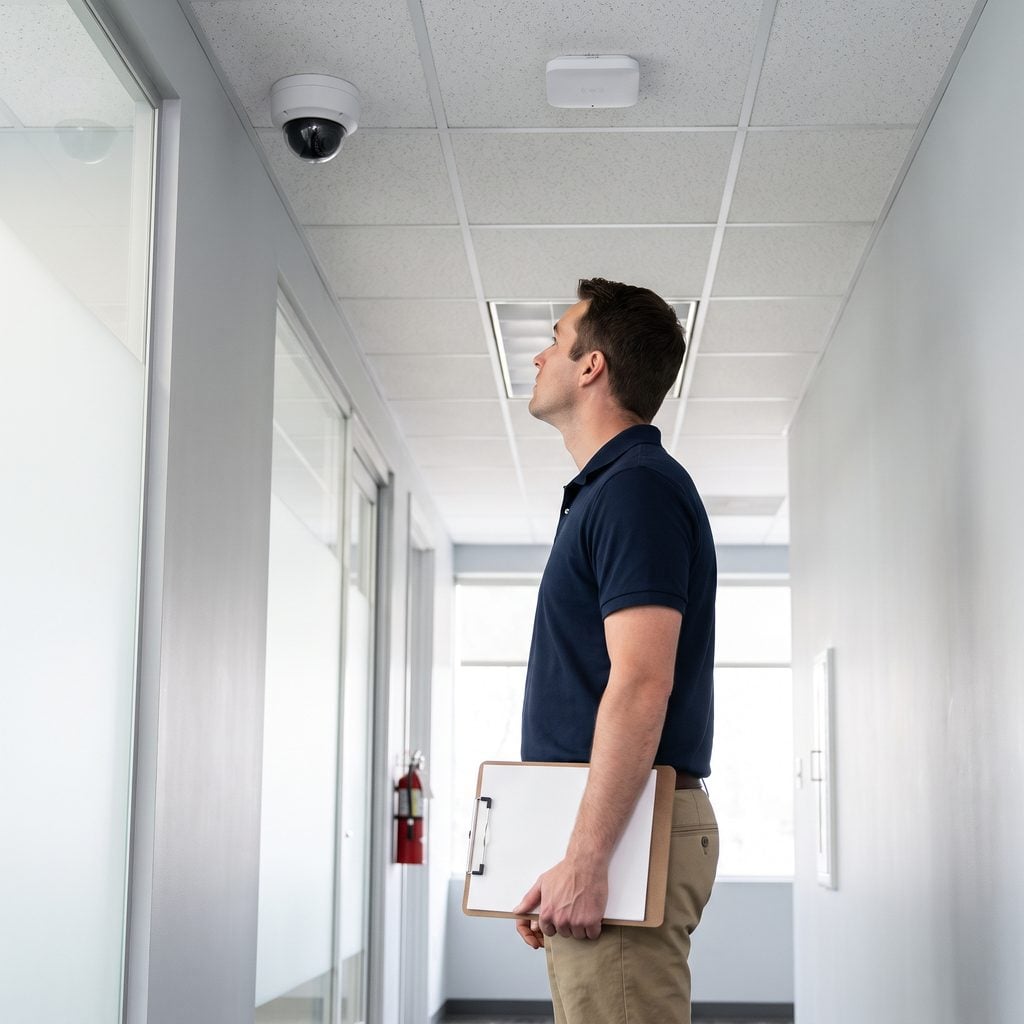
Then we walk the building. We look up, not just down: at access points, cameras and equipment that should not be there or should be locked away. Massachusetts 201 CMR 17.00 expects records containing personal information to be kept in locked facilities with restricted physical access, so we check how server closets and records rooms are secured, whether with locks, access control or cameras. We then review the findings with you and what to fix first.
Compliance That Holds Up to an Audit
Massachusetts 201 CMR 17.00 requires a written information security program from any business that owns or licenses personal information about Massachusetts residents. Triton writes and maintains that program against your actual environment, not a template.
For healthcare providers and business associates, we implement the HIPAA Security Rule’s technical safeguards. For manufacturers and research groups in the defense supply chain, we build the System Security Plan and the 110 NIST SP 800-171 requirements that CMMC Level 2 assesses. We also produce risk assessments and policies, usually within one to two business weeks once we have the information we need. Hold nothing back: an incomplete disclosure can leave you exposed with your insurer.
Compliance is not a destination. It’s a continuous operating standard. Any firm that treats a passed audit as the finish line is one configuration change away from a violation.
Case Study: Ransomware at a Global Manufacturer
A manufacturer with plants in several countries relied on a co-managed IT arrangement that had left its defenses years out of date: a firewall past its 2022 end of support, no multi-factor authentication, no endpoint protection on any computer or server, an out-of-support VMware vSphere 6.7 environment and a flat network where every device could reach every other one.
When a ransomware group targeted the company late on a weekday, we connected over VPN and worked through the night. With Axiom, our AI monitoring system, we removed the attackers, stopped the encryption within hours, locked down the firewalls and rerouted traffic to prevent reinfection. We then walked the executive team through a timeline measured in seconds and minutes.
The company moved from co-managed IT to fully outsourced IT with Triton. It now meets its insurance and compliance requirements for the first time, and once its real security posture was on record with its insurer, the savings more than covered the cost of our contract.
Why We Keep Our Client List Private
Security isolation starts with us. Triton never publishes client names or logos, because a public client list tells attackers which organizations share one provider and hints at the stack each one runs. If one of them were ever targeted, the list would point straight to the next. Keeping every relationship private protects all of our clients, including you. References are available during an evaluation.
We also do not sell dark web monitoring. Dark web monitoring is a notification service, not a security strategy. Given the scale of data breaches over the past decade, your organization’s information is already exposed. The correct investment is proactive hardening, not a monthly alert telling you something you cannot change.
Backups and Insurance Paperwork, Done Properly
Restore tests that prove recovery
Backups run on Datto and Triton Online Backup, stored in AWS, Wasabi or other S3-compatible storage depending on where your data must live. We run documented restore tests on the schedule your compliance requirements set, and keep the records for your audits.
We deliberately restore to different hardware or platforms than the original, and change the method from test to test, so recovery still works if a device or vendor disappears.
Cyber insurance applications
Insurers now ask the same detailed technical questions. Our management platform pulls accurate answers from your live systems, and we complete the technology sections of your application or renewal: controls, software, vendors and risk assessments. Your team adds business details such as revenue and titles.
It is a paid service, and it costs far less than months of back-and-forth emails, with no risk that the answers on file differ from what is deployed.
Incident Response From Down the Street
Our response to a security incident usually begins within an hour. We identify what happened, understand its scope, quantify the impact and then act: the affected device is isolated, evidence is preserved, and our engineers work the incident from our Worcester office. If someone is needed on-site, they come from Harvard Street.
After every incident you receive a written report with the timeline, the root cause and the changes that prevent a repeat, documented for your cyber insurer and for Massachusetts breach notification under Chapter 93H if it applies.
More Triton services in Worcester: Computer support and services · IT support and help desk · Network installation and support · Managed IT services in Worcester
Worcester Cybersecurity: Common Questions
What cybersecurity services does Triton provide in Worcester?
Sophos Firewall and Sophos Endpoint XDR, 24/7 security monitoring, Proofpoint email security and awareness training, multi-factor authentication, least-privilege access, network segmentation, backups with documented restore tests based on your compliance requirements, incident response and compliance documentation for 201 CMR 17, HIPAA and CMMC.
Is your security assessment really free?
Yes, for prospective clients. It is read-only: a Microsoft 365 review of about a day, an internal network sweep of about a week, and a physical walk-through of your building.
Do you monitor security around the clock?
Yes. Every managed client is monitored 24/7 through our security agents and monitoring software, and Sophos security staff can reach us after hours. Alerts that indicate an active threat trigger an emergency response.
How fast do you respond to a security incident?
Our response usually begins within an hour. We identify, understand and quantify the event, then act to contain it, and we document every step for your insurer and regulators.
Can you help us comply with 201 CMR 17?
Yes. We write and maintain the written information security program the regulation requires, and we implement the technical and physical controls it calls for, such as encryption, access control and secured storage, in your actual environment.
Do you support CMMC Level 2 preparation?
Yes. We help defense suppliers build the System Security Plan, implement the 110 NIST SP 800-171 requirements and prepare the evidence for whichever Level 2 path your contracts require: a self-assessment or a certification assessment by an authorized third-party assessor (C3PAO).
Which backup platforms do you use?
Datto and Triton Online Backup, storing data in AWS, Wasabi or other S3-compatible storage, chosen by where your data is allowed to live. Restore tests are documented on the schedule your compliance requirements set.
Which security awareness training do you use?
Proofpoint Security Awareness Training for clients who want ongoing training, and yearly Sophos training for organizations with lighter compliance needs such as PCI.
Why doesn’t Triton offer dark web monitoring?
Because it tells you something you already know. Years of large data breaches mean most organizations’ information is already circulating. We put that budget into hardening your systems instead of paying for alerts you cannot act on.
Will you help with our cyber insurance application?
Yes, as a paid service. We complete the technical sections from your live systems, so the answers on your application match what is actually deployed. See our cyber insurance readiness service.
How Triton Delivers
The Sophos XDR Mandate
We deploy Sophos Firewalls as the non-negotiable perimeter standard. Any firm operating without synchronized endpoint protection is an insurance liability. Sophos Endpoint (EDR/XDR) is the mandatory internal security layer.
AWS Scalability
We deploy on AWS because downtime is not an option. When a critical system goes down, AWS support responds with enterprise urgency, not a ticket queue. Every dollar of downtime is a dollar your IT provider owes you an answer for.
The AI Autonomous Advantage
Axiom, Triton’s proprietary AI monitoring system, gives our engineers real-time visibility that off-the-shelf tools cannot replicate. It is not for sale, it is how we deliver.
Founded in 2001
25 Years of IT Expertise
Serving New England
5 Regional Offices + Dublin & BVI
Under 10 Minute Response
84th Percentile · MSPbots Verified
Sophos Silver · Microsoft Solutions Partner
Security & Cloud Partners
HIPAA · CMMC · SOC 2 · PCI
Multi-Framework Compliance
Let's Discuss Your IT Needs
Triton Technologies delivers managed IT services, cybersecurity, and IT support for businesses across New England. Contact our team today to start a conversation about your technology environment.